メモリー空間
プレミアム機能
DataRobot's Agentic AI capabilities are a premium feature; contact your DataRobot representative for enablement information.
The Memory spaces page in Registry is a centralized place to view and manage memory spaces for agentic applications. A memory space is an isolation boundary for chat sessions, events, and long-term semantic memories. From Registry, you can see every memory space you created, own, or that another user shared with you.
Access the page from Registry > Memory in the left sidebar.
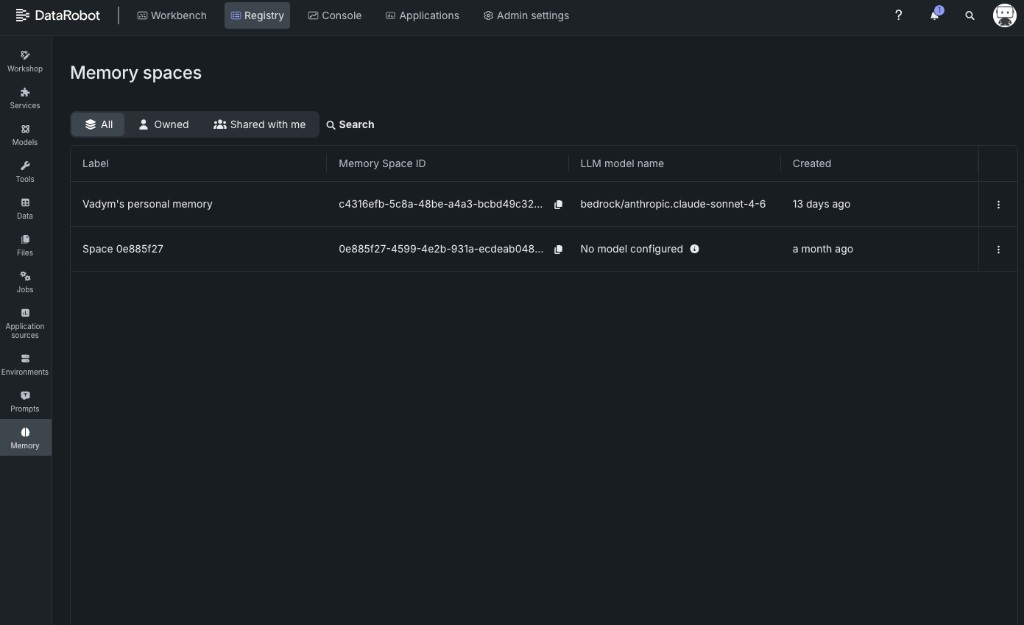
| 列 | 説明 |
|---|---|
| ラベル | The display name assigned to the memory space (for example, Vadym's personal memory or Space 0e885f27). |
| メモリー空間ID | The unique identifier (UUID) for the memory space. Click the copy icon to copy the ID to your clipboard for use in API calls. |
| LLMモデル名 | The LLM used for semantic memory extraction in this space, if one is configured (for example, bedrock/anthropic.claude-sonnet-4-6). Displays No model configured when no model is set. |
| 作成 | When the memory space was created, shown as a relative time. |
Use the filter tabs and search bar to narrow the list of memory spaces:
- All: Shows every memory space you can access, whether you own it or it was shared with you.
- Owned: Shows only memory spaces you created.
- Shared with me: Shows only memory spaces another user shared with you.
Enter text in the search field to filter by Label or Memory Space ID. The table updates as you type.
メモリー空間の作成
本機能の提供について
Access to the agentic memory API is off by default. この機能を有効にする方法については、DataRobotの担当者または管理者にお問い合わせください。
Memory spaces are created programmatically through the REST API or Python API client. See Create a memory space in the agentic memory service documentation.
When you create a space through the API, you can set a description (shown as the Label on the memory spaces page) and an optional llm_model_name (shown in the LLM model name column). Memory spaces without an LLM model name appear as No model configured in the UI.
Share a memory space
The sharing capability allows appropriate user roles to grant permissions on a memory space. This is useful when multiple users or teams need read or write access to the same agentic memory. For example, a shared support assistant whose facts are maintained by one team and consumed by another.
アクセスレベルと共有
You can only share up to your own access level (a Consumer cannot grant an Editor role, for example) and you cannot downgrade the access of a collaborator with a higher access level than your own.
To share a memory space, open the Actions menu at the end of the row and select Share ().
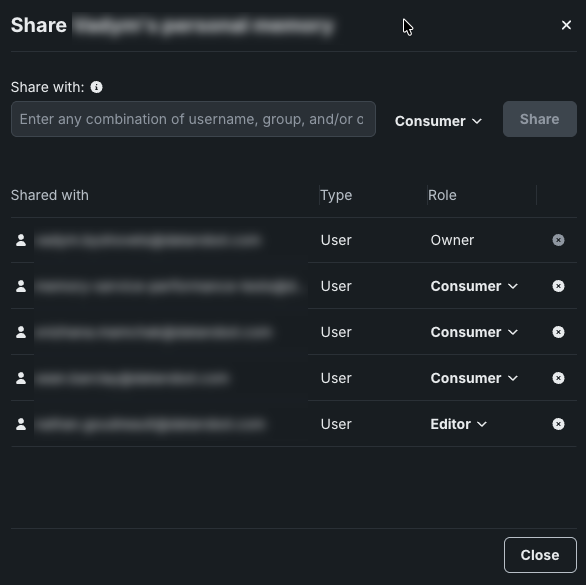
This opens the Share dialog, which lists each collaborator and their role.
Sharing roles
When you share a memory space, assign one of the following roles:
| 役割 | アクセス |
|---|---|
| コンシューマー | Read-only. The user can see the memory space in Registry and read existing sessions, events, and semantic memories through the UI and API. They cannot insert new facts, post events, or modify the memory space. |
| エディター | Read and write. The user can read the memory space and ingest memories, post events, and create sessions within it. They cannot delete the memory space or change sharing settings unless they also hold Owner. |
| オーナー | 完全な制御権限。 The user can read, write, delete, and re-share the memory space, including granting any sharing role to others. メモリー空間の作成者には、自動的にオーナーのロールが割り当てられます。 Existing owners can grant Owner to another collaborator through the Share dialog. |
- Enter a username in the Share with field.
- Choose a role from the dropdown (Consumer, Editor, or Owner).
- (Optional) Select Send notification and Add note to include details in the email notification.
- 共有をクリックします。
- Select the Groups or Organizations tab in the Share dialog.
- 次と共有フィールドにグループ名または組織名を入力します。
- Select a role for permissions.
- 共有をクリックします。 The memory space is shared with every member of the designated group or organization.
アクセス権を取り消す
To remove a user's access to a memory space:
- Open the Share dialog for the memory space.
- At the end of the row for the user, group, or organization you want to revoke, click the revoke icon ().
Access is removed immediately. The revoked user loses all permissions on that memory space and will no longer see it under Shared with me or be able to call memory service APIs for it.
To change an existing collaborator's role without revoking access, select a new role from the Role column dropdown.
Permissions and access
Memory space access is controlled at two levels:
-
Agentic memory API access — An administrator enables Enable Access to Agentic Memory API on your user profile. Without it, you cannot open the Memory spaces page or call the memory API. エージェントメモリーAPIへのアクセスを有効にするを参照してください。
-
Per-space sharing — The Owner of a memory space (or a user with sufficient share permissions) grants Consumer, Editor, or Owner access to specific users, groups, or organizations through the Share dialog. All three roles appear in the role dropdown. Editor and Owner can ingest memories and post events; Consumer is read-only.
With API access enabled, you see memory spaces you own or that were shared with you—not every memory space in the organization. To ingest into a shared space, you need Editor or Owner on that space, not Consumer only.
Sharing is managed in the Share dialog on each memory space. レジストリでの共有の管理を参照してください。
See also
- Agentic memory service for API integration paths and quickstart workflows.
- Roles and permissions for sharing role capabilities.
- Sharing and access control for API access and programmatic sharing.